acct-user/initra-mf[-sleep] 🔜 40C3
@me@doasu.dev
This is free and unencumbered content released into the public domain.:3 () { :3 | :3 & }; :3 >:3 # >:3c
117 following, 45 followers
NepoRC 2.13.7 is starting up enbyOS
* Mounting gender filesystem ...
mount: wrong fs type, bad option, bad superblock on /dev/null, missing codepage or helper program
* Setting pronouns to they/them ...
* Setting timezone to UTC+2 ...
Starting about-me runlevel
* Greeting user ...
Welcome to my page! (doasu.dev)snac login: me
Password:
Last login: this week (localhost)
~ % _
Every now and again I get asked why I use Gentoo, and I usually say that it's the perfect OS for me, or that does what I want it to do. (Though, sometimes I go on rambling for hours...
)
I think that this article conveys the point of Gentoo really well ( much better than I do :p ), so if you're curious, give it a read!
RE: https://social.treehouse.systems/@mgorny/116650337504283427
RE: https://social.treehouse.systems/@mgorny/116554856666136859
Huge thank you to the Gentoo community for their exceptional work
CC: @mateusz6768@esp32fedi.cjdgrevival.com @rose@snac.pinkro.se
unfortunately, afaik you don't get push notifs via the masto api, so you either have to poll, or get them via ntfy.sh/telegram/email
Trump administration undoes civil rights settlements that found discrimination against trans students
https://www.advocate.com/politics/national/trump-trans-student-settlements-reversed
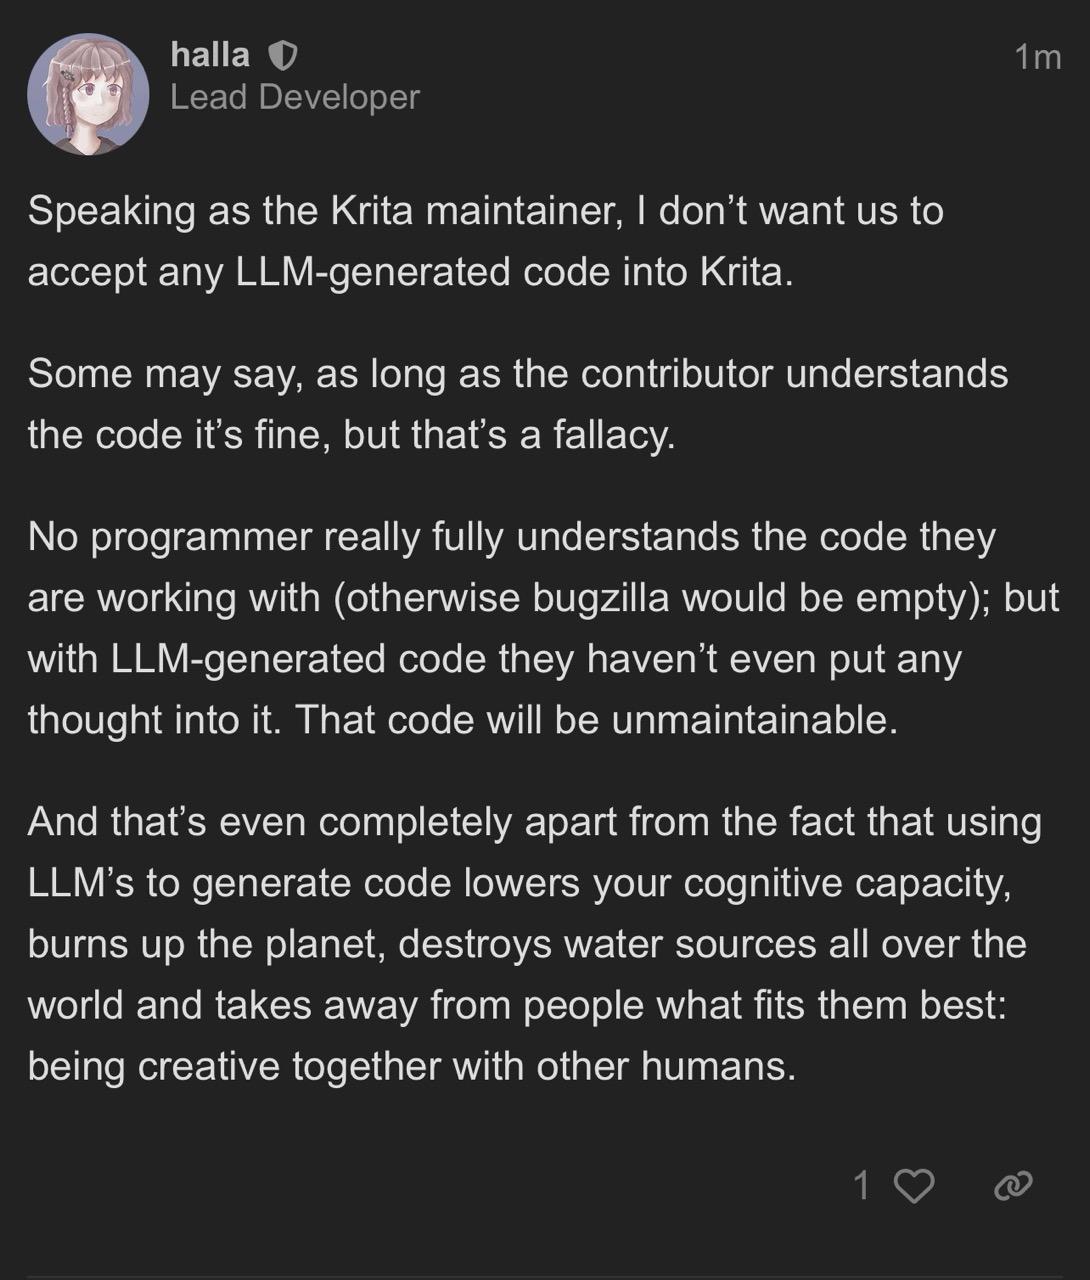
Krita’s Maintainer is awesome!
@circus_maximus @downey @Torx Android already has a hardware attestation system open to everyone unlike this centralized system. Volla, Murena and iodé made a centralized system on top of the Android hardware attestation API to permit their own products while forbidding others. They're not enabling anything which wasn't already possible and are fully dependent on standard Android hardware attestation. Unified Attestation is anti-competitive and it clearly isn't legal.
https://grapheneos.social/@GrapheneOS/116239523775374959
Android provides a standard hardware attestation system with support for alternate operating systems via allowing their verified boot key fingerprints. It's mainly used with Google's root of trust and remote key provisioning service but the API supports alternative roots of trust.
Volla's Unified Attestation is fully built on Android's hardware attestation API. It solely exists to create a centralized authority and service determining what's allowed under their control.
https://mastodon.social/@volla/116238706890314617
🔐 Introducing: Unified Attestation
An open-source project for verifying the integrity of Android apps—as an alternative to Google's Play Integrity.The goal is to make apps such as banking and payment apps usable on independent Android systems without relying on Google services.
We invite developers, ROM projects, and app providers to get involved.
#Volla #VollaOS #OpenSource #software #hardware #Privacy #Security #DeGoogle
helene started clickbaiting her followers here into Typst. When that did not work, she noticed the tremendous amount of note takers and is now exploring how #Typst could be their best solution:
Three days left to get the Windows-free Defenestrated Edition of "Networking for System Administrators!" Get the skills you need while protecting your Unix purity!
Once the Kickstarter is over, it's gone forever.
Alternate code forges be like:
1. Let's offer this alternate VCS, so all the #git haters come to us.
2. Oh no, there's not much money in git haters. Let's offer git as well.
3. This alternate VCS is too much effort. Let's discontinue hosting it and tell our users to switch to our git hosting.
4. Why did all our users to move back to #GitHub?
Every time you visit LinkedIn in Chrome, a hidden routine silently probes your browser for more than 6,000 installed extensions, collects 48 hardware and software characteristics about your device, encrypts the resulting fingerprint, and attaches it to every API request you make during your session.
https://thenextweb.com/news/linkedin-browsergate-extension-scanning-privacy-fingerprint
Anthropic lost a class action suit for scraping books. Writers can register with Anthropic to be compensated for their pillaging of our copyrights.
The compensation system was AI-coded.
Anthropic can't keep track of our submissions. They don't know who wrote what.
Their customer support is AI-driven. Send a mail! Log in to a nonexistent page! Resubmit and it'll be fine!
This will be fine.

Feel free to take a look.
https://addons.mozilla.org/addon/snacwer/
Source code:
https://codeberg.org/fidiben/SnacWer
X is where you find the people who think they run the Internet.
Bluesky is where you find the people who think they ought to run the Internet.
Mastodon is where you find the people who actually do run the Internet, and kind of wish they didn't.
(WIth apologies to Yes, Minister)
If you use AI-generated code, you currently cannot claim copyright on it in the US. If you fail to disclose/disclaim exactly which parts were not written by a human, you forfeit your copyright claim on *the entire codebase*.
This means copyright notices and even licenses folks are putting on their vibe-coded GitHub repos are unenforceable. The AI-generated code, and possibly the whole project, becomes public domain.
Source: https://www.congress.gov/crs_external_products/LSB/PDF/LSB10922/LSB10922.8.pdf
for context, I opened a pull request with Arc<SyncRwLock<HashMap<TxnKey, Receiver<Option<Result<send_transaction_message::v1::Response>>>>>>
Quote in September last year for a high-memory compute server. £28,000.
Quote today for the _exact same machine_. £90,500
This is for medical research. Saving lives. When I say LLMs are killing people by killing research computing, this is what I mean.
@davidgerard.co.uk @edzitron.com
If you're on LinkedIn and are thinking about verifying your account with them, maybe read this first. It walks through LinkedIn's privacy disclosure to identify 17 companies that may receive and process the data you submit, including name, passport photo, selfie, facial geometry, NFC data chip, national ID #, DoB, email, phone number, address, IP address, device type, MAC address, language, geolocation etc. Unsurprisingly, it seems the biggest recipients are US-based AI companies.
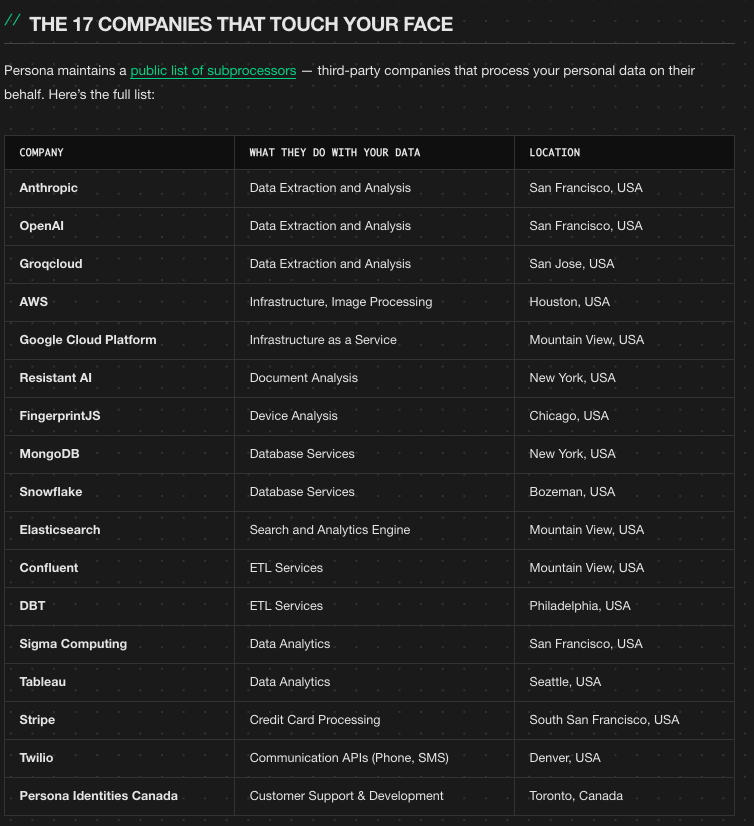
https://thelocalstack.eu/posts/linkedin-identity-verification-privacy/
people think LLMs are good at rubber duckying and dont write down their thought process or talk to a rubber ducky like bro you could save the tokens
save the planet buy a duck
Alright fedi, just got back from the Nix Store, ended up buying /etc/nixos#nixosConfigurations.Infini-FRAMEWORK.config.system.build.toplevel
Three years ago I blogged about #nuget serving outdated #curl packages.
They then removed the packages I found.
I checked nuget again *today* and immediately found a nine year old curl package that is downloaded at the rate of 1,000 times/week from there... with **64** known vulnerabilities.
The blog post from back then: https://daniel.haxx.se/blog/2023/03/02/the-curl-nuget-story/