acct-user/initra-mf[-sleep] 🔜 40C3
@me@doasu.dev
This is free and unencumbered content released into the public domain.:3 () { :3 | :3 & }; :3 >:3 # >:3c
117 following, 45 followers
NepoRC 2.13.7 is starting up enbyOS
* Mounting gender filesystem ...
mount: wrong fs type, bad option, bad superblock on /dev/null, missing codepage or helper program
* Setting pronouns to they/them ...
* Setting timezone to UTC+2 ...
Starting about-me runlevel
* Greeting user ...
Welcome to my page! (doasu.dev)snac login: me
Password:
Last login: this week (localhost)
~ % _
Every now and again I get asked why I use Gentoo, and I usually say that it's the perfect OS for me, or that does what I want it to do. (Though, sometimes I go on rambling for hours...
)
I think that this article conveys the point of Gentoo really well ( much better than I do :p ), so if you're curious, give it a read!
RE: https://social.treehouse.systems/@mgorny/116650337504283427
RE: https://social.treehouse.systems/@mgorny/116554856666136859
Huge thank you to the Gentoo community for their exceptional work
the piano has a metronome that resets when my phone decides to kill the piano app
@mkljczk android issues?
@PabloveSky more like issue with the piano, i think losing bluetooth connection shouldn’t reset metronome settings
> 'XD’ is a commonly used Polish emoticon. Different capitalisations and the number of xs and ds influence the meaning. It was adopted from the West’s usage as an expression akin to 😆 when Poland properly embraced the internet in the 2000s, but unlike in the West it didn’t slide out of fashion and adopted more general, varied usage among Poles. Sometimes it is also used as a noun.
https://fedi.vale.rocks/objects/d1dd659a-53b8-4815-b850-04731f602a1d
Question to the people who fully (or most of the time) work from home: how do you keep going with your personal projects after work? Do you have another computer on a different part of the house, or do you roam with your laptop, or you don't care and you just sit inside the same four walls most of your day and evening? If something else, please comment.
I personally do everything in one space, so there are some periods of time when my projects or my home lab maintenance lag behind, simply because I don't want to sit in that office anymore. How about you?
#HomeLab #SysAdminLife #WorkFromHome @homelab
| Have another desk somewhere else: | 0 |
| Walk around the house with a laptop: | 0 |
| Same place, all the time: | 0 |
| Something else, let me explain: | 0 |
@badnetmask @homelab @homeassistant work laptop and then different PC or laptop for personal projects based on what I want to work on. I did used to share the desk for everything but eventually it makes me hate sitting at that desk so I spend a lot of time with laptops in different spaces to try to avoid association with work that impacts my mental state on the others
Philip Mallegol-Hansen [He / Him] » 🌐
@philip@mastodon.mallegolhansen.com
@badnetmask @homelab @homeassistant There’s a room in my house that is “the office”, all serious work happens in that room.
The desk is set up with a USB-C dock so I can easily rotate between computers at the same workstation.
Yes, my desire to do personal projects is definitely lower than it used to be. But I don’t think changing the physical space would help with that. There’s only so many hours a day I can look at code. So they mostly happen on weekends.
@badnetmask @homelab @homeassistant same setup in general like sometimes having a meeting on the couch while having a very good setup at my desk. BUT a different computer for work and home. The most crucial thing in my eyes to keep it mentally separated
@badnetmask @homelab @homeassistant I have a different account on my laptop to keep things separated. I also tend to go to the pub to work on personal stuff as sometimes motivation can be an issue.
@badnetmask @homelab my home office is de best room in the house. its my living room. My wife has the other living room, with the fireplace.
im glad i didnt fall for the codeberg meme
If you don't like that, you're encouraged to host your own instance. That's the whole point. (Forgejo can run on an RPi with no problem.)
Plus, there's ongoing research into cross-forge collaboration/federation, so that it'd no longer matter which instance you use. So #Codeberg folks could still contribute to your not-allowed-on-Codeberg project.
See: https://codeberg.org/forgejo-contrib/federation
CC: @nullenvk@yourwalls.today @pengwius@mastodon.world @nat@blahaj.pl
Codeberg are fully permitted to say what is welcome in their house and what isn't. The techbros can vibecode themselves a git repo, no one forces them to host any particular place.CC: @nullenvk@yourwalls.today @pengwius@mastodon.world @nat@blahaj.pl
We placed a tracking device in a shipment of rare books to see which AI company was buying it, and found an Amazon facility where Amazon scans and destroys books.
GitHub going down is like a snow day.
I was done with my hours today anyway 😅
We use GitLab at work - but the build still pulls down packages from GitHub ofc so... 🤷
@sarajw I found myself expecting to find a really sneaky rhyme hiding in the last two lines.
When #GitHub UI is so broken that you can't mark a pull request ready to review when merge status can't be loaded, so you need to actually do that via API.
Self hosted email continues to steeply decline over decades. I know exactly why this is happening. These big providers send most self hosted emails to spam. Then, managing self hosted email itself requires a good amount of technical sysadmin knowledge. Top reasons I think:
1 IP/domain reputation
2 Cloud/VPS IP reputation
3 Misconfigured SPF, DKIM, or DMARC hurts deliverability.
4 Incorrect DNS setup
5 Spam-like sending patterns etc
there are some good books by @mwl if you want to understand sysadmin topics and email hosting. Give it a try. Link https://mwl.io/nonfiction
Does anyone still use #Snac software?
@the_coffee_lover yes! I
set up a #snac instance just a few weeks ago.
It’s been purring along nicely, without ever giving me any trouble.
@me@doasu.dev Awesome. How long have you been using it?
らくがき
らくがき
らくがき
らくがき
boostedらくがき
らくがき
らくがき
らくがき
Zazwyczaj na Niebezpieczniku informujemy o smutnych sprawach, ale dziś informujemy o sprawie wyjątkowo smutnej. Wczoraj odszedł Paweł "kravietz" Krawczyk, jeden z pionierów polskiego IT security i prawdziwy hacker w dobrym tego słowa znaczeniu.
Paweł zawsze chętnie dzielił się wiedzą, inspirował setki osób i swoimi działaniami oraz kodem realnie wpłynął na stan polskiego cyberbezpieczeństwa. Był też mocno zaangażowany w budowę krakowskiej społeczności bezpieczników i aktywnie udzielał się w sieci. Lata temu na stronie ipsec.pl, ostatnio także na Twitterze i Mastodonie.
Pawła będzie mogli pożegnać 21 sierpnia o 13:00 w kaplicy na cmentarzu w Batowicach (ul. Reduta w Krakowie).
PS. Pracowałem z Pawłem ramię w ramię przez kilka lat. Przegadaliśmy wiele wieczorów i nocy. Przez ostatnie 20 (!) lat dyskutowalismy o różnych tematach. Jego spojrzenie na wiele kwestii było nieszablonowe i dające do myślenia. Będzie mi Pawle brakować tych skłaniających do poszerzenia horyzontu rozmów.
dpd timeout
ipsec down
Do zobaczenia po drugiej stronie tunelu Kravietz!
-- Piotrek
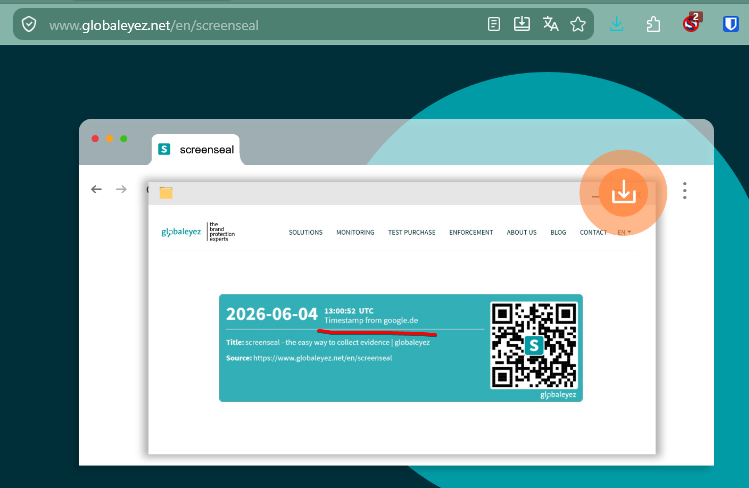
i came across the globaleyez's screenseal tool, which claims (on the cws page) to capture "authenticated, tamper-proof, and admissible in court" screenshots
a quick investigation shows that this is not true! (from my personal understanding, i am not making a legal claim here)
first of all, you can *intentionally* tamper with the evidence - the screenshots are captured client-side, so there is nothing preventing you from using the "inspect element" browser functionality to change the content on the page. in a similar vein, the extension's rendering code itself could be modified to watermark any date/title/source a malicious party desires.
but what if the "tampering" here is referring to the site operator? it is also trivial to detect the screenseal tool capturing a page and change it dynamically (see video demo). in addition, you can detect whether the extension is installed and active in the first place.
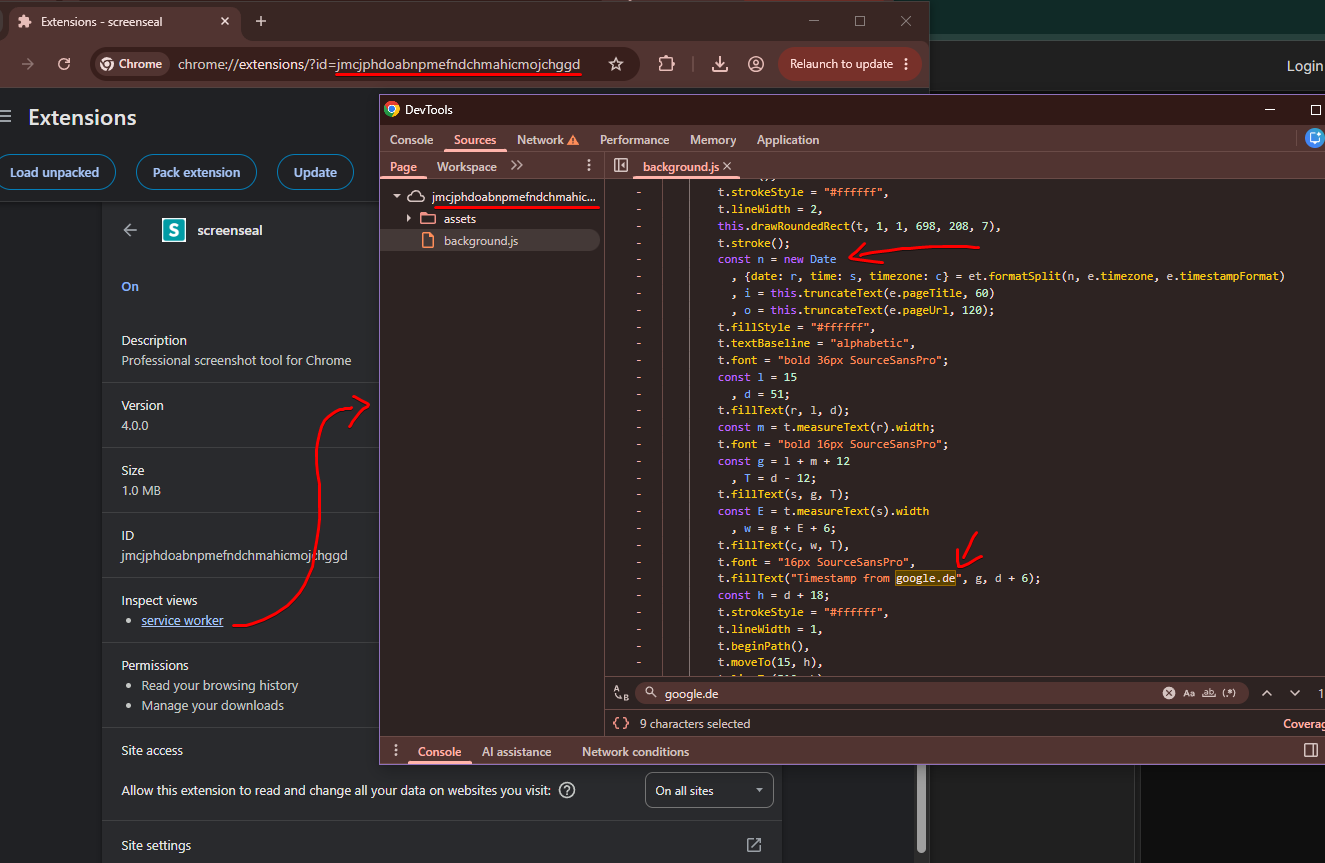
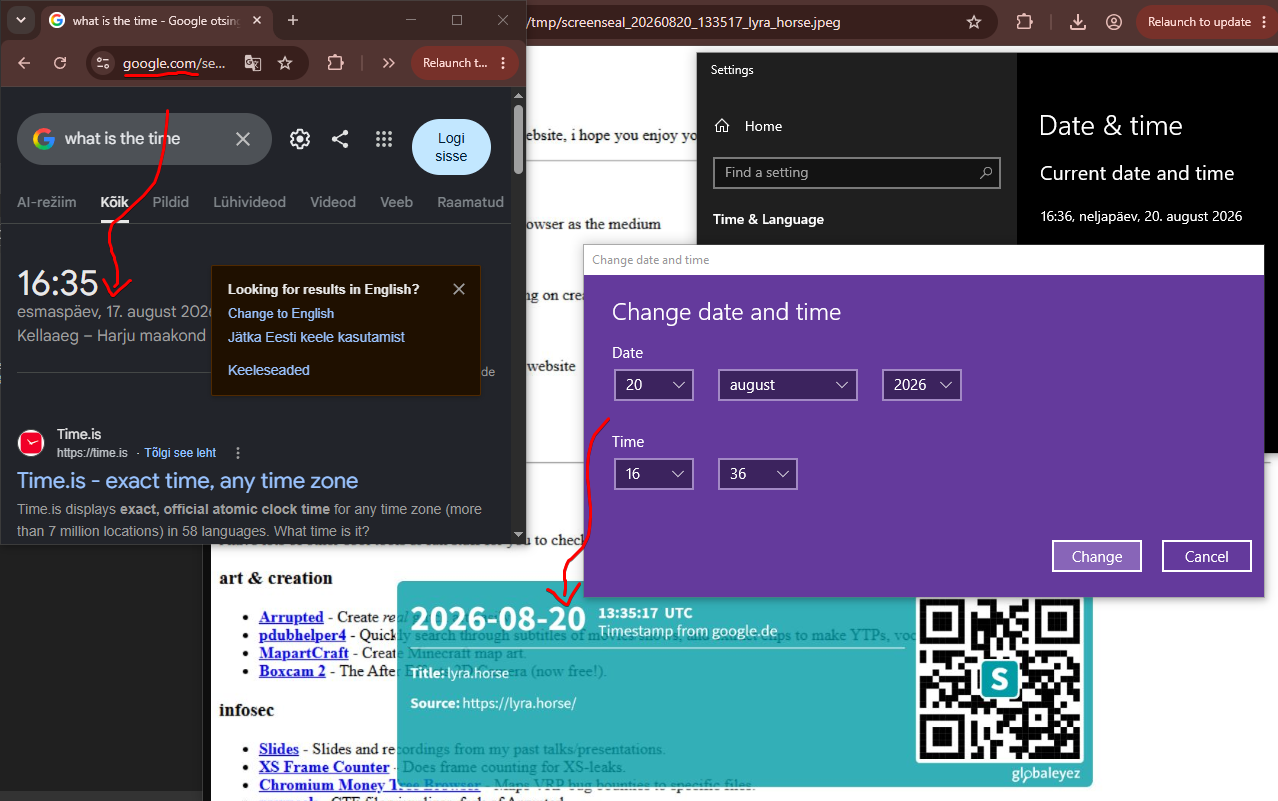
but imo the worst part here is that the tool straight up lies about the timestamp being from google - looking at the extension code in chrome's built-in devtools, we can see that the "timestamp from" string is hardcoded and the timestamp is actually retrieved with the javascript "new Date" constructor. this means that you can fake the timestamp by just changing the system date yourself.
this is kind of really bad because if you're using this tool in good faith, relying on it to fetch the correct timestamp from an external server, you may end up *accidentally* producing misleading evidence if your system time is set incorrectly.
idk, this tool actually seems *fine* for what it is - a free website screenshot tool with an embedded timestamp and url, and seemingly good motives (i didn't find any telemetry/tracking/subscriptions, it probably exists to get their own brand in front of more (global) eyes)
i think these mistakes are likely a result of miscommunication between marketing/management/developers, i've emailed globaleyez about these findings in hopes that they will update their claims and the timestamping logic to not be misleading - lets see how they respond
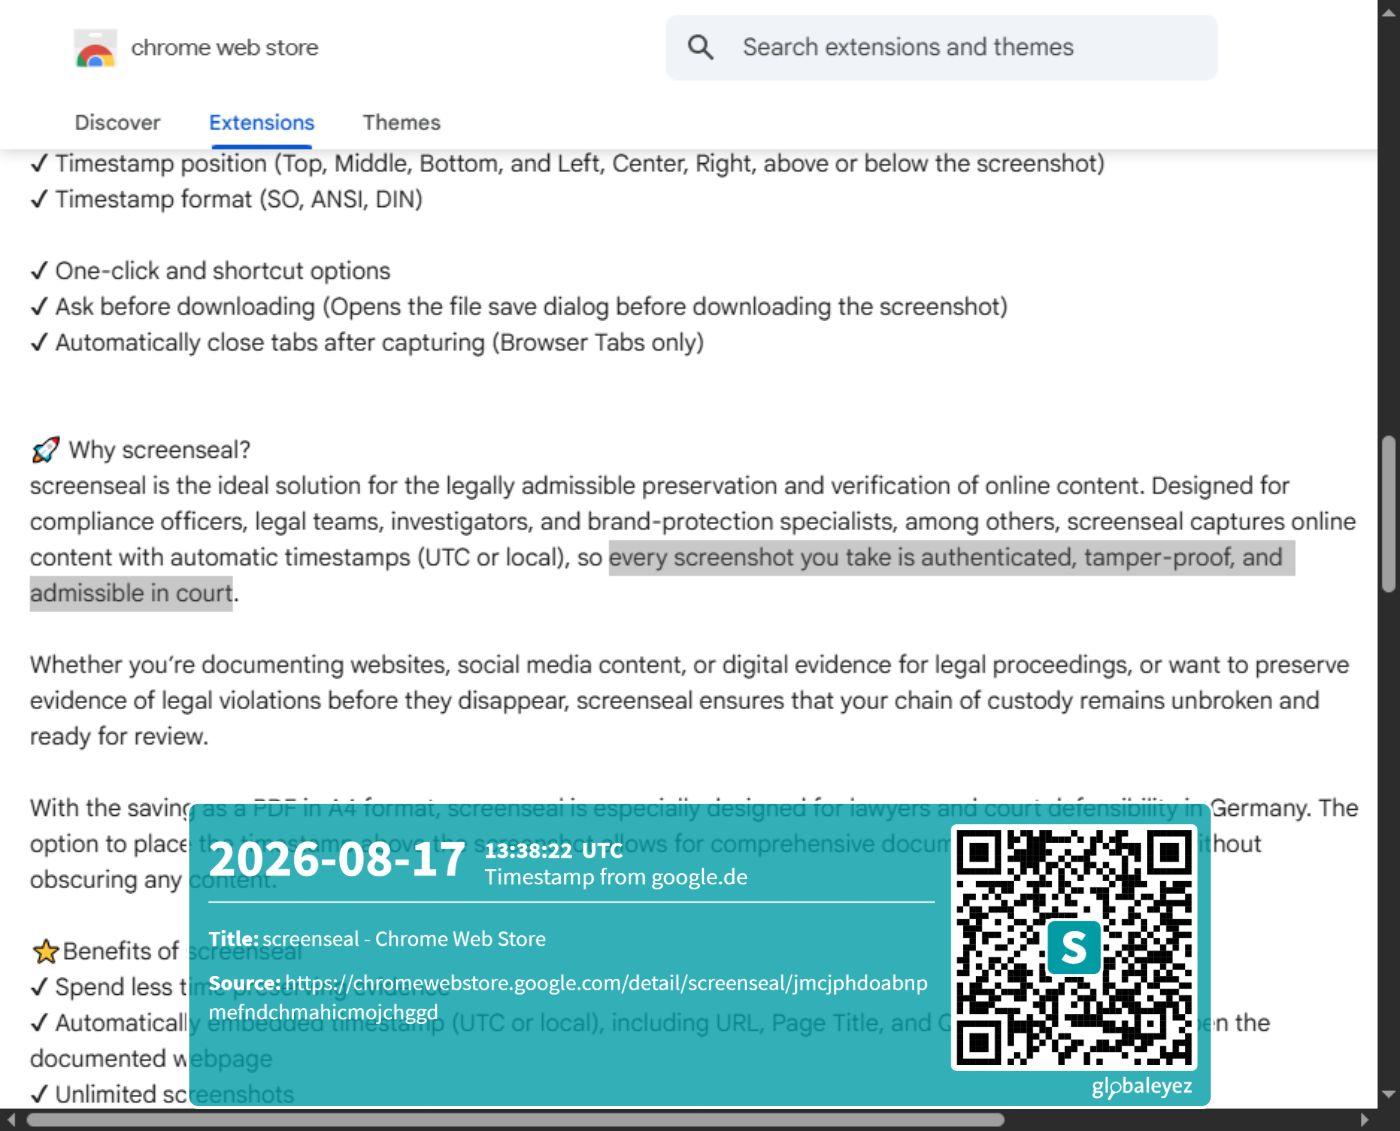
@rebane2001 Where is the server-side timestamp claim? I don't see it in CWS listing, and their website seems to have the same text too: https://www.globaleyez.net/en/screenseal
@AlesandroOrtiz on the screenshots themselves - you can see it on the example screenshot on the page
@rebane2001👍🏻 I somehow missed it, was focused on the CWS description.
I want to hear from a lawyer whether this would get any cases thrown out (probably not unless there's further evidence of actual tampering by party using the screenshots).
Probably would lead to some level of court sanctions or reprimand when globaleyez is using it in their own court cases, though.
I am shocked. Nobody could have seen it coming. Nobody, I tell you!
https://futurism.com/future-society/college-critical-thinking-ai
> As one New York financier told Financial Times journalist Gillian Tett, new hires who were seen as “AI natives” are turning out to have alarmingly shallow ideas. So much so, the anonymous finance worker admitted, that his firm now actively avoids seeking out AI-literate STEM graduates, and opts to comb through humanities students instead.
Oh, the humanities!
@rysiek hmpf.... artificial is not intelligent, it's pattern recognition, it's statistical gambling, it is NO LOGIC, no reasoning, not even smart or creative.
@rysiek I am so sad for students who have been deprived of an education and even worse atrophied critical reasonong skills. Academia has wronged them by tolerating this technology, let alone encouraging them to depend on it. They are the victims of a horribly unethical human subjects experiment. The worse is yet to come in tje years ahead, as children come of age having never once learned how to learn.
@naruciakk @cczona this piece by @ploum is very on topic:
https://ploum.net/2026-01-19-exam-with-chatbots.html
@rysiek I actually hate this sense that kids are supposed to come almost fully formed into their workplace, ready to do amazing things on graduate wages. You want them to do groundbreaking, deep thinking? Model it. Teach it. Cultivate it. Pay it.
@Iwillyeah it's not about being fully formed. It's about having the capacity of critical thinking. That *is* something the education system – from elementary schools all the way up to universities – should be cultivating, and it is clearly failing at that.
Critical thinking is so much more than job training. It is necessary for a healthy, vibrant society, for effective political debate, for so many more things. We *should* be alarmed that people exit the education system struggling with it.
Leszek [singular masculine/masculine animate/animate neutral depending on the grammar of your language] » 🔓
@makdaam@chaos.social
@rysiek Last time I checked most of the elementary to high school education (except STEM) was repetition, memorization and pattern matching. Any kind of original thought was punished.
This was shown perfectly when LLMs were able to pass any "humanities" exam or homework. It was scary talking to polish and history teachers who didn't see this as an example of how the schools are failing for decades. In most cases it was seen an issue with students not memorizing everything themselves.
@Iwillyeah
@rysiek what can I say. The tune hasn't actually changed much in the 20 years I've been teaching. The next level has always complained that the level before them has failed to adequately prepare young people to progress to their level. Companies have been doing the unthinkable and wildly unorthodox thing of actually hiring arts graduates into non-arts roles for as.long as i can remember. Maybe it's really different this time, but the rhetoric is just not that new.
@rysiek @Iwillyeah It's failing because it's not trying. There's an idea that they always use to gaslight that overwhelming people with useless information and repetitive exercises to reproduce it verbatim will somehow let them develop critical thinking, but that's not now learning works.
If you want to develop critical thinking, you engage in activities that involve crticial thinking, not drill random crap that is the inverse of that if anything
@rysiek I am not sure if this also relates to the USA now being a rogue state with controlled media, a government so shallow as never seen on earth with horrifyimg morals?
@rysiek I think my late career will have something similar to the "cobol effect" back in pre-2000.
(for those who are not aware: year 2000 caused a major headache in legacy IT systems with date length, esp. old and effectivly non-replaceable systems running on Cobol. If you knew the language back then, you earned a shitload of money.)
@rysiek "AI natives" are these new hires from the future or do hiring execs just not understand the word native.
@rysiek Thank you for posting this. My daughter is in a humanities program in college and she frequently feels anxious that she’s making the wrong decision. She actually reads the material and writes without using assistance of AI tools, something she enjoys outside of classes. I’m going to show her the article you boosted and your amusing comment. Below is evidence of her diligence in studying for exams during the semester 😆 #AI #studying
@rysiek meanwhile, here I am, almost failing my thesis course because I loathed doing research but I managed to pass because my teacher forgot to grade a section of my whole file, lol.
I would rather write a creative story than do research ever again. Fuck that shit.
@rysiek I'd be curious about the details of how this works: I can see people who went for the typically-less-lucrative degree out of genuine interest being more likely to have done their own work; but if it's just genuine interest that makes you do your own work there are STEM enthusiasts available as well.
Is it a sorting problem, with those genuine enthusiasts harder to distinguish from botherds who scored better? Is it an actual disciplinary rot problem and those departments fell faster?
@rysiek @purplepadma This is why schools who rush to integrate AI into every aspect of their curriculum are just so ridiculously short-sighted. It’s almost like they’re also full of alarmingly shallow ideas. Go figure.
Im experiencing it in the workplace, people with an attitude that think they can google and copilot in 10 minutes the engineering gut feeling and craftsmanship you build in a career…
@rysiek Surprised humanities doesn't have the same problem. Must be lagging a little bit?
Now that there's interest in that field, albeit not intrinsically, maybe it'll get the attention it needs to catch up :p
@rysiek Be wary of any news story that prompts a "see I told you so" reaction. Confirmation bias aside, this story does not address all the non-STEM students using AI too.
hey, "AI native" people:
what do they need you for?
turning yourself into a small markov chain chat script, and thinking you have an employable future repeating what you asked the AI, is a joke
no one will notice?
no one will simply say:
"if that's all you do, what do we need you for?"
there is no way to "integrate AI into your workflow"
you have to have skills that *mean something*
turning yourself into a plastic moron means you're eminently replaceable
by #AI
@rysiek
My wife was at work one day, her colleague came to her with an issue: printer not printing. She asked him what had he done so far, and he says: "scatgpt just had me go down a list and nothing worked. "
She goes down to the printer and asks the user a question: "when did you start having issues? "
Turned out, user unplugged everything to move around, then plugged the cable in the ethernet port and not USB. Wife confirmed this, fixed it, and printer ejaculated jobs.
@rysiek This is not bad news.
... In fact, I'm going to be talking at my alma mater government-and-international-studies high school in October and I may work this anecdote in, because I already intend to say something to the effect of "they gave me an undergrad BS degree from one of the more prestigious tech unis with one class of intro philosophy, one class of intro econ, and a safety factors class I dropped before midterms under my belt, and maybe that's a problem."
@rysiek As if "humanities" students were immune against using AI instead of thinking by themselves...
@rysiek @briankrebs I have a BA in English, yet do DFIR and my incident reports are better for it. I always have a narrative with a protagonist and rising action, unfortunately there’s not always a satisfying resolution…
@rysiek but they want us to use AI and agents to code to keep our jobs?
The reason the techbros were pushing social media addiction and ai slop is because they want to infantilize the fucking masses. They do this because then they can feel superior.
Only what they're doing is destroying society as a whole, and soon the techbros will be facing a massive mob of violent people and none of their technology will work.
@rysiek when the plagiarism machines started doing well on some standardized tests we could have taken it as a sign that this way of teaching and grading is broken, instead it was used to fuel the bubble. Oh, well, at least they are creating some amazing value for shareholders.
@rysiek It is so incredibly depressing to think that there are however many thousands or myriads of colleges and universities in the United States, and let's throw in high schools as well because the hi-power high schools posture themselves as basically the onramp into higher #education, have gone all-in on this "AI literacy" nonsense. Can we please take the concept of literacy away from the techlords now? Please?
@rysiek 4+ years of job hunting shows that bosses, in fact, reject the concept of critical thinking as a general skill.
And oh boy do I have things to say about the depth of ideas coming out of long-established C suites 😬
@rysiek I don't think it's AI.
If you ask these kids what they want to be when they grow up, they don't say doctor or teacher or fireman. They say "I want to be rich". Money was always a means to an end, but now it's an end in itself. These kids have grown up in a world where the people who should be in jail are raping their classmates, because they are rich, because they are powerful. The people they admire and respect are barely scraping by. The mask slipped during covid and now they know the only escape from the capital monster is to be the capital monster.
These kids aren't AI pilled. They're CEO pilled. That's why they're dumb.
@rysiek This isn't totally new. Mumblemumble decades ago, a friend of mine in SF, who headed up the local office of international tech firm told me he'd rather hire humanities/artists than those who only trained to coder because you can teach a creative to code, but not the other way around necessarily. That's why this new focus on AI for coding - maybe the grunt work - but then how do people learn - has me rolling my eyes. It takes intelligence and creativity to build things. Not AI vibes.
@rysiek @tantramar When even the finance bros think you’re shallow? That’s the ultimate dubious achievement. 🤣
RE: https://loops.video/v/hvWYLmfg_B
The AI graduation speech they didn’t show you at Tech Bro Bootlicker Central!
”Fuck AI!”
”College graduation speakers across America are telling you need to master AI for the future. I’m here to the mission of your generation is to destroy AI. Kill it!”
”I think your generation’s battle won’t be humans against AI. It’s gonna be people with substance vs people with shallow knowledge. It’s going to be mastery versus faking it. It’s gonna be people with good taste vs tacky.”
Hear hear!! 🔥
KDE is turning 30! 🎂
Celebrate with us at the #Akademy2026 social event with good food, drinks, music, and plenty of KDE birthday fun activities.
Let’s celebrate three decades of KDE together. 🎉
A bunch of "hackers hacked" stories in my timeline today. 🙄
Reminder: the more you (journalists and editors working at media companies) misuse the h-word to make your story sound 👻 scary 👻, the more you entrench the idea that the problem with security of our day to day devices is that there exist people who have technical skills and are able to break into them – rather than the fact that their manufacturers don't give a crap about security, making that easy.
And the less secure we all become.
This also has knock-on effects for the AI hype BS.
If all stories focus on the actors able to break into things, rather than companies who fail to secure their stuff (often in most basic ways), then of course OpenAI and Anthropic get to exploit that to pump hype before their IPOs.
Instead of what should be happening, which is Anthropic and OpenAI facing hard questions about why they failed to sandbox their crap effectively, leading to multiple security incidents.
And, this is also how two years after CrowdStrike b0rked update took down innumerable systems – including at airports and hospitals, one wonders what the human cost of that was! – nobody faced any real responsibility for that.
Words matter. Narratives matter. Journalists and editors should understand this.
"Hackers hacked a thing" reporting is journalistic malpractice.
@rysiek I followed some very cynical advice that someone who’s been in this industry for longer than me gave: I bought shares in ClownStrike and sold them six weeks later, for a 50% return. The advice was: whenever a big company has a cybersecurity incident, their stock price dips and recovers within three months because there aren’t actually any long-term consequences. So I look at their pre-dip price, buy the shares, and set them to be sold when the price is slightly above the pre-dip value.
I did the same thing with UNFI (I think this one actually took three months to recover to the pre-dip value).
Both shares are currently trading at well above what I sold them for (I don’t normally hold shares unless I understand their business, so I have no idea if these are actually companies with reasonable long-term business models, but they didn’t seem to suffer at all financially from their incidents).
@rysiek It seems all too common nowadays that journalists and editors will gladly report narratives directly from the press release of major companies, like Oracle laying off many thousands of people, not because they're bleeding money, but because "AI" makes them more efficient. I wonder if the pace required to be quick to report a thing also means critical concerns about responsible reporting get thrown out the window.
@munin oh that has a name too – "CEO said a thing" reporting
they're not journalists. they're stenographers.
there's an insult in the welder community and it's "i'm gonna buy you a grinder for Xmas". this is an insult because a good welder makes good welds not requiring any grinding.
we should be telling these "journalists" "i'm gonna buy you a stenograph for xmas"
@rysiek
I'm from the 80s and I am repeatedly confused as to why people think constantly connected devices would ever be fully secure.
Like, these devices are plugged in to the entire planet all the time, they're secure until someone on the planet finally breaks it's security. 😖
@rysiek in my experience most people claiming they were hacked had incredibly poor security practices, and vibe coding is making it worse
⏩︎VOTE⏪︎ ᶜʸⁿⁱᶜⁱˢᵐ⁼ᵃᶜᶜᵉᵖᵗᵃⁿᶜᵉ (Ben Royce) » 🌐
@benroyce@mastodon.social
OH LAWD HERE THEY COME
EL1T3 HAXX0RS
it's easier to play at lazy stereotypes than convey accurate meaning
Those in power want the masses to view people with any skill or expertise (technical or otherwise) as the enemy. If our societies truly valued knowledge and expertise, those currently in power would be in trouble as they lack both.
@rysiek "And pretty soon anyone with a raspberry pi will be able to use an AI to break into your bank or your home video monitoring software to watch your kids change. We can't even barely keep a handle on the things ourselves!!! Something must be done and we know what that needs to be."
gim » 🌐
@gim@lou.lt
@rysiek shifting responsibility. Given it seems to be much worse than it was, it begs the question: is this intentional
If the media actually put the blame of poor security practices on the shoulders of businesses then it might affect share prices, and that would somehow be worse than actually attempting to fix the problem.
The latest propaganda is "It's the Iranians"
Before that it was the Chinese
Why, exactly aren't we air-gapping infrastructure control systems again?
@rysiek Can confirm. The worst part of working in that industry is the clients who'd get upset about findings and demand they remove or downgrade them.
One asked for CVSS scoring and blew a fuse when half the report was CVSS 10.
It's sad that we could have software as well-built as some of our bridges, but it's spoiled by profit, greed and "gotta go fast" culture
RE: https://ec.social-network.europa.eu/@EUCommission/117047406016279929
Reminder to USAians that the US banking sector being shit and not being able to process transactions in a sane way – thus creating the conditions for shitty band-aids like cryptocurrencies or venmos – is largely a matter of choice on part of the legislators and regulatory bodies.
@rysiek Mostly the legislature, but same difference.
@whvholst fair point
@rysiek @whvholst I do have some hope that the Fed will do something useful. FedNow shows they are finally copying some of the ECB playbook for TARGET/T2.
https://en.wikipedia.org/wiki/FedNow
(But it can be argued that the ECB stands a chance only because the EC previously had some strong antitrust action to make payment processing less abusive. So, your point stands.)
@rysiek A lot of Americans are surprised to learn that Venmo and similar popular commercial services don't exist in Canada, and then even more surprised to learn that they don't because there would be no market for them. Anyone with a bank account in Canada has access to Interac Direct E-Transfer, which has existed for ages, doesn't charge huge fees (I think some banks charge a small per-transaction fee, but many waive it), and is ubiquitous.
At least in the USA I can *use* my bank without needing a creepy proprietary phone app. I just need a browser, a password, and either an email or a phone, and if I choose the phone option then even a 50-year-old land phone will suffice.
I don't need a proprietary app to ride a bus, either. Cash or a bank card will do. I think there's a city or two where you don't even need that.
Don't act superior. You've got bigger problems than we do. We still have some privacy; you have none.
@argv_minus_one I also don't need creepy proprietary apps for any of that. 🤷♀️
And claiming having better privacy in the US is… certainly a take!
One of the main complaints about open-source phone operating systems is that banking apps don't work. I always found this confusing, because I just ignore the app and use the bank's website, but I learned recently that most Europeans aren't allowed to do that. The app is mandatory.
I too had been under the impression that privacy was a big deal in Europe. I've been repeatedly shocked and horrified over the past few months by revelations like this.
It's my understanding that the EC also intends to impose age verification on most of the Internet, also to be conducted through a phone app (EUDI Wallet) that requires an unmodified proprietary operating system.
This would make open-source phones effectively illegal. You can have one, but it can't access anything.
Without open source, there is no privacy.
@argv_minus_one you are explaining this to a person who writes a regular column (in Polish) about this sort of thing, and who had been a privacy and digital human rights activist for over a decade and a half.
I am well appraised with issues around privacy in the EU. I am also well appraised with issues around privacy in the USA.
Even with all the high-profile dumb ideas of European Commission, the privacy situation in EU is leaps and bounds better.
@argv_minus_one currently age verification laws are *already on the books* in a bunch of US states for example:
https://en.wikipedia.org/wiki/Social_media_age_verification_laws_in_the_United_States
Yes, and that is an abomination. But those laws do not require the use of a proprietary device. You're still in control of what you reveal, when, and to who.
A proprietary device could be recording and reporting everything you say within range of its microphone, and you'd never know because the public can't see the code. As horrible as US social media age verification is, that's even worse.
@argv_minus_one what in the world are you smoking and where can I get some? Is this insane hypothetical mandatory proprietary EU device in the room with us right now?
Because systemd changes to allow for age verification, made explicitly because of *existing* US laws, are:
https://github.com/systemd/systemd/pull/40954
The proprietary device I speak of is discussed here: https://github.com/eu-digital-identity-wallet/eudi-app-android-wallet-ui/issues/287
The systemd change you mention adds a date-of-birth field to the local user database, and…that's it. It does not enforce or even implement the collection of that information, nor does it involve anything proprietary.
We do have some state laws mandating the collection of that information, namely in California and Illinois, but that still doesn't require anything proprietary.
Then I'd appreciate an explanation, because I'm honestly worried sick about Europeans like you.
@argv_minus_one the explanation is you might want to diversify your information sources, as it seems like you are getting a pretty lopsided information stream about the actual situation in the EU.
Yes, there's a bunch of dumb ideas floating around, and yes there are serious concerns related to them, and yes enforcement is sometimes spotty, but that does not erase all the privacy preserving stuff that is already in effect in the EU.
@argv_minus_one time and again there is a story about how Apple or Meta or Google or whoever make a big thing about not releasing or at least delaying some AI boondoggles in the EU because of privacy laws; they try to frame it as EU citizens missing out, but the predominant response I've seen is "good riddance".
Meanwhile, same AI boondoggles are long deployed in the US of A.
Didn't the EC just waive the fine for a major breach of EU privacy law? What good is a privacy law if it doesn't actually protect you?
@rysiek @mycotropic Remind me of time spent working at a US fintech company for banking cores. They had made something that could do everything a bank wanted in real time without needing to schedule batch jobs or anything. Banks actually PUSHED BACK on this idea and asked for stuff to be done in batches on a schedule instead, and thus the product was effectively degraded to something worse.
@rysiek
My big bank prediction is at the FDIC will be gutted, and probably already has been. The oligarchs can't stand to see any money lying around for the purpose of protecting the little people. They have to own ALL the money. Social security medicare, retirement funds, bank accounts...every last penny.
I'm not quite old enough to have lived through bank failures and bank runs, but I think we're all going to get the opportunity in the years to come.
@rysiek Couple of stories about American banking, admittedly going back decades.
(1) I once went on a business trip to the USA with an American who was based in Norway. He had to use TRAVELLERS' CHEQUES in his own country!!
(2) As a student I heard of European kids who spent the summer working in American summer camps. At the end of the summer they'd pick up their pay cheque, get on a Greyhound bus, and try to cash the cheque a few days later when they ran out of cash. Only to be told that the cheque was only good in the town where it was issued!!
(We were used to British cheques being honoured anywhere in the UK, and various systems whereby they'd work anywhere in Europe. Cheques that only worked in a tiny area, not across the whole country, seemed really weird.)
help wanted
https://lake.computer/blog/help-wanted/
«
I am very sorry that the software that I created & put online for free, without any warranty, explicit or implied, has not met your expectations. You are entitled to a full refund. I have taken the liberty to initiate it. You should already have it.
»
i wonder if you could make a useful DOS executable with just emoji
one intriguing possibility is that several UTF-8 emoji codepoints start with 0xF0 which is an otherwise harmless prefix on 8088
💯 -> f0 9f 92 af
this becomes
00000000 F0 9F lock lahf
00000002 92 xchg dx,ax
00000003 AF scasd
Although you're stuck with 9F it seems, so you're constantly trashing AH by calling lahf. If we accept this as a constant side effect, we can just use half of the bytes.
unfortunately you kinda need AH to call interrupts...
so let's identify some useful emoji.
here's NOP:
🐐
there are 3717 of these. surely some of them have to be useful
unfortunately i don't see any that begin with F0 9F B0-BF
that would have been nice, since that would have given us mov reg,imm
A lot of other emoji start with E2, which is a LOOP instruction - not particularly useful there, but maybe we can use E2 to complete another instruction. we also have E3 which is JCXZ. i'm drawing a blank.
0️⃣1️⃣2️⃣3️⃣4️⃣5️⃣6️⃣7️⃣8️⃣9️⃣
are all potentially useful ALU operations though!
these are "keycaps" and i don't know if they are technically emoji. but like, i figure if theyr'e in color they're emoji. that's my qualification.
you can't make this shit up
the hourglass is FWAIT
why am i doing this. i have other projects
because the world needs an emoji-based LLVM backend
all you really need, technically, is a small loader and emoji-encoder, then you just let Turing do all the work
jackpot: 😮 gives us
cbw
scasb
that's incredibly useful. now we can increment a pointer.
👁️ gives us
xchg cx,ax
sub di,8FB8h
the xchg is just noise.
the subtraction however is interesting. it's equivalent to adding 7048h.
48h actually seems like a plausibly useful number
😪
gives us stosb. Now we can increment DI and we can write to it. oh baby
🐸.
🐸 is the goddamn key to this whole thing
it's
F0 9F 90 B8.
the first three bytes are essentially a 3-byte nop, but it ends on B8.
B8 IS MOV AX, IMMEDIATE.
i love u frog
i want to print "HELLO"
how do we calculate hello if we can only use +1 and +48
you're never gonna believe me but guess what the hex ascii code for H is
we need a pointer into CGA video memory at segment B800.
☺️ gets us us B8EFh in DX. Good enough. It's about 3,824 bytes down the screen but we're using god damn emoji for assembly language here so i'm not too picky
ok how do we even initalize something to 0?
8F F0 is an undocumented alias for POP AX.
guess what DOS pushes to the stack for you when your COM program starts.
that's right. a 0. now we have 0 in AX.
i was worried that this was going to be too stupid to be plausible, or require something like 32KiB of brainfuck-level shenanigans, but i actually think this is going to work
demo coders who compete in size coding categories know a lot of clever tricks that take advantage of how DOS intializes a program's PSP.
les bx,[bx]
at the start of a DOS program gives you a usable pointer to VGA video memory.
no really. how does this work? it ends up accessing a value in the PSP. DOS puts the value 0x9FFF there. used as a segment, that's only 16 bytes from the start of VGA memory.
you can work around that.
this is not related to emojissembly but i think its cool
i would like to propose new demo party categories.
512 byte demos? yawn.
512 emoji demos? now we're talking
okay. to write HELLO somewhere on the screen we have an additional issue in that we have to account for attribute bytes, we can't just yeet out the string HELLO as much as i'd like to and we already know calling int 21h or int 10h is off the table because we trash AH every instruction.
we can probably just increment di twice to skip the attributes. or if its easier to generate a visible attribute byte i don't really care what color the letters are
okay hear me out
you know how LAHF is trashing AH constantly? how i figured that was annoying but ignorable?
... what if we fucked with the flags so that every time we executing LAHF it put a visible attribute byte in AH
i mean it doesn't have to be an attribute byte. i was just assuming AH would be garbage but we actually do control the value. sort of.
WE HAVE AN H
the crap on the screen is CGA snow. it's happening because i end up looping over the whole thing and i'm not waiting for blanking periods to write to video memory. the CGA's DRAM is single-ported and this makes it upset
i usually like staging but DosBox-X's 8088 emulation is more accurate.
why am i not using my own emulator? because it's a low level emulator and i have to reboot the entire machine when i hang the CPU. which i am doing. a lot.
someday i'll have save states and that won't be a problem...
🐰 and 🐎 are now essential to this operation
oh, there's your problem right there. you forgot the horse opcode
... i really need to work a cow into here somewhere, don't i
🐄 is TEST which is fairly useless but also probably pretty easy to make into an effective no-op. which is sort of lame, but hey.
🐮 is SCASB though, that's got some promise, but i don't really need to read anything...
well, i can use it to increment di somewhere.
okay, now i just have to cook.
i think it's okay if i put crap on the screen other than HELLO as long as you can read HELLO
i mean that technically counts right
i'm not a fancy computer scientist person, but i think it's a fair assessment at this point that emoji are, in fact, turing complete
The following is a valid DOS COM executable that prints "HELLO" in the lower right corner of the screen.
You can copy these emoji into a text editor, and save it as EMOJI.COM. it should be 141 bytes.
It will run in DosBox-X, with the following options:
cpu cputype=8086
machine cga
🐸☺️🐰🐎♐🗃️🧯🧯🧯🐮💗🦮♐🐰🐹🗃️🧯🧯🧯🧯💗🪗🧯😗🧮😗🧮😗🐮😪😔⭐
may god have mercy on my soul.
Here's a screenshot if you just want to take my word for it.
you may notice one of the letter L's is green. the green color comes from the flag register, because i really wanted to use one of those LAHFs for something.
My demoscene-friend Trixter informs me that this is sadly unlikely to become a sizecoding category, because if the history of ASCII executables is any indication, someone would just make a converter at some point
If you want the disassembly, here it is!
I like how I make a neat tool and immediately do the most obscene thing possible with it.
so.. EmojiDOOM wen?
could you actually make EmojiDOOM?
One problem is that executing emoji becomes exponentially harder once you stop targeting the 8088.
The 386 also has the lock prefix - but it enforces validity. Only certain opcodes are "lockable" and if you stick a LOCK prefix on an incompatible opcode you get an int 6 #UD exception. Guess which mnemonic isn't lockable. LAHF :(
No bueno.
Now, thankfully, insane folk like @sqpat have ported DOOM.. yes, the full version of DOOM to the 8088 real mode architecture.
The question is if that herculean effort can accommodate the code bloat that translating to emoji will inevitably entail.
The relentless LAHF opcodes are just really, really annoying too. AH is a rather important register to have continually trashed, although we can pretty easily set it to either 00 or FF via CBW.
Also I checked ... the INT 10h instruction CD 10 to even change video modes does not appear in any of the 3,945 emoji i searched. We would have to generate the code for it and jump to it.
with emoji.
in short you would have to be utterly insane, or @foone
@gloriouscow @foone
If you strategize carefully and maybe had insider help you might do an #emoji proposal or two targeted at making #Doom happen
I believe all the code points are there waiting to be used
They just don’t present as emoji (or any other character) yet
So if you know what you want you could build towards that
You can post unreleased emoji and they show up as boxes until your OS is updated to display them
DOS might not care, but unsatisfying until #Unicode approves them
Really cool remote tech for good job alert! Signal is hiring an android dev:
- Global remote working US timezones
- Working in Kotlin and Java
- Working on open source privacy preserving product
- $160,000 - $260,000
https://jobs.lever.co/signal/9a3ac9b5-1b59-4bdf-a0a9-fd008fd55d40
#FediHire
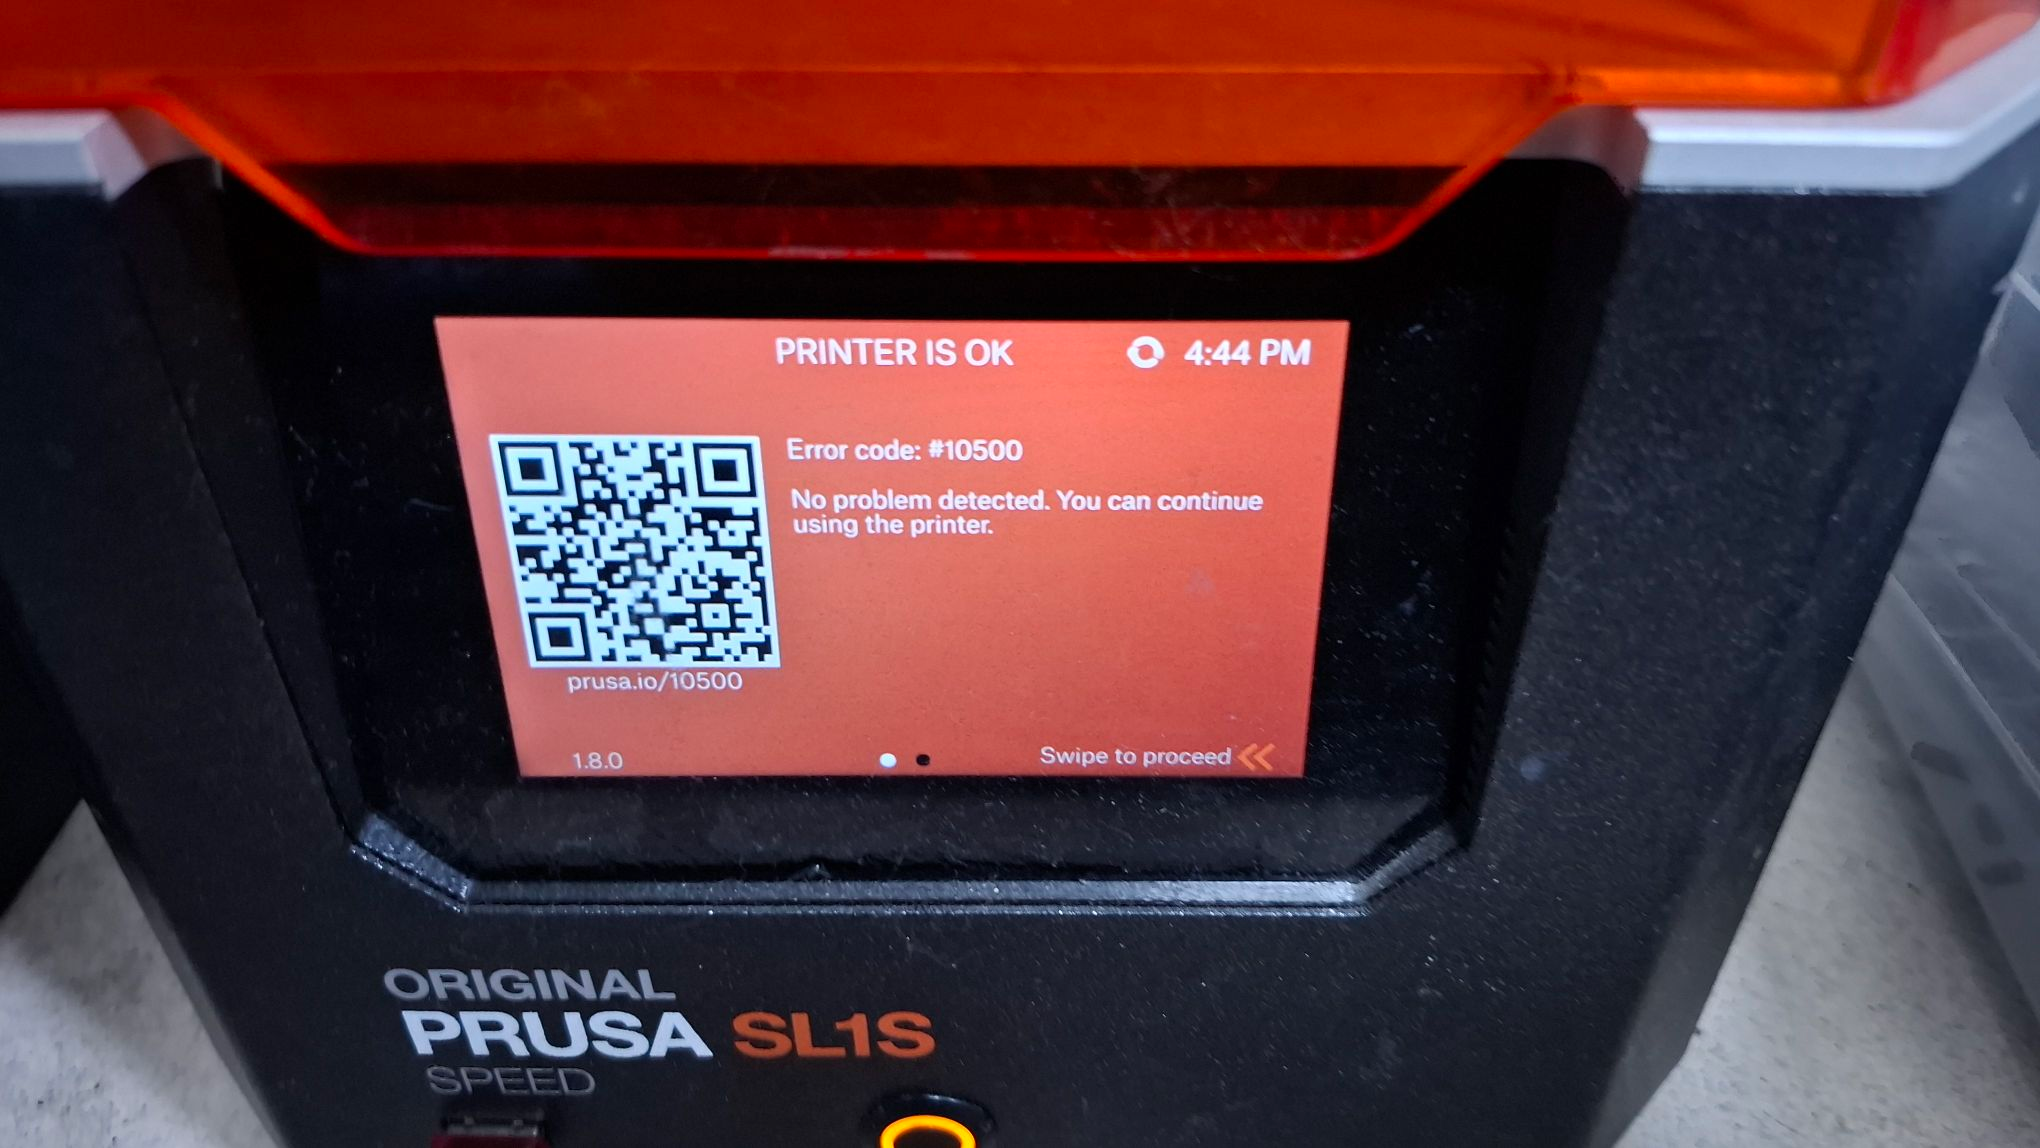
3d printers are so full of errors, they're going to error out when there's no error, apprently.
Courtesy of a Prusa SL1S at @hswaw
released by IBM in 1981, sturdies were a massive flop
Do you like RiBs?
Rewrites (of Rust projects) in bash, I mean.
@mgorny I would like to see some Rust projects rewritten in POSIX C, maybe even K&R style. As a "social experiment" or something.